


A single pane of glass for understanding and mitigating risks across your entire codebase and supply chain.
Cost / License
- Freemium
- Proprietary
Application type
Platforms
- Software as a Service (SaaS)
 United Kingdom


Proscan AppSec is described as 'Unified application security platform — 12 scanners including SAST, DAST, SCA, and pen-testing in one on-premise deployment. Replaces your entire AppSec stack' and is a vulnerability scanner in the network & admin category. There are more than 50 alternatives to Proscan AppSec for a variety of platforms, including Web-based, SaaS, Windows, Linux and Self-Hosted apps. The best Proscan AppSec alternative is GitHub, which is free. Other great apps like Proscan AppSec are SiteOne Crawler, Burp Suite, OpenVAS and Nessus.
A single pane of glass for understanding and mitigating risks across your entire codebase and supply chain.
United Kingdom
PrivJs Safe helps secure projects by blocking the installation of vulnerable javascript packages. PrivJs Safe also provides an ESLint plugin @privjs/eslint-plugin-safe to actively detect the import of vulnerable npm packages in the projects.


The most proven open source scanning solution to help organizations understand their license compliance and security vulnerability risks.
 United States


WP Triage watches your WordPress sites and highlights the plugins and themes most likely to cause trouble, so you can fix them first.
 New Zealand


 Norway


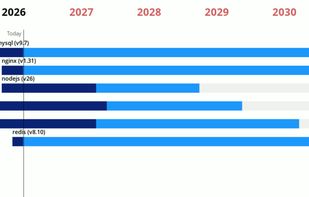
Security vulnerability and end-of-life prioritization for every web development team. Identify what needs attention across every website and application, prioritise upgrades earlier, and lead better customer and stakeholder conversations.
New Zealand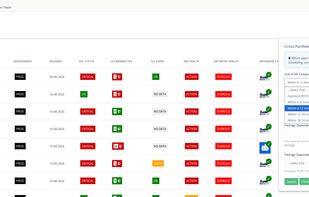


Timesys Vigiles is a Software Composition Analysis (SCA) tool that helps generate and analyze a Software Bill of Materials (SBOM) for publicly known cybersecurity vulnerabilities, particularly CVEs. Vigiles is optimized for embedded systems, and it provides a complete...
United States


vet is a tool for protecting against open source software supply chain attacks. To adapt to organizational needs, it uses an opinionated policy expressed as Common Expressions Language and extensive package security metadata including:
 India


FlexNet Code Aware is a free code scanner that scans Java, NuGet and NPM packages looking for license compliance, IP, and security vulnerability risks.


Konvu automates vulnerability triage. It checks exploitability conditions against your code and environment, produces evidence-backed verdicts, and pushes results back to the tools you already use.


SecDash automatically detects security vulnerabilities in applications created with ChatGPT, Claude, and other AI tools, providing clear and actionable guidance.
 Brazil


Dependency Update Automation for npm, composer and docker made easy. Check your git repositories for vulnerabilities now!.
 Germany
 EU


