




CertWatch
Like
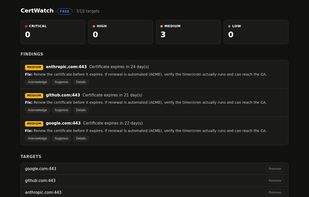
CertWatch is a self-hosted TLS monitor that ships as a single Go binary with SQLite - no database server, no agents, no telemetry.

Cost / License
- Freemium
- Open Source (Apache-2.0)
Application type
Platforms
- Self-Hosted
- Docker

Features
CertWatch News & Activities
Highlights All activities
Recent activities
- Nizar-Tuanku added CertWatch
 Nizar-Tuanku added CertWatch as alternative to Uptime Kuma, StatusCake, Uptime.com and Super Monitoring

CertWatch information
Developed by
Nizar TuankuLicensing
Open Source (Apache-2.0) and Freemium product.Pricing
free version with limited functionality.Written in
Alternatives
9 alternatives listedBadge
Get an embeddable badge for CertWatchSupported Languages

AlternativeTo Categories
Security & Privacy, Network & AdminGitHub repository
- 0 Stars
- 0 Forks
- 0 Open Issues
- Updated


No comments or reviews, maybe you want to be first?