


Scanner for vulnerabilities in container images, file systems, and Git repositories, as well as for configuration issues and hard-coded secrets.
Cost / License
- Free
- Open Source (Apache-2.0)
Application type
Platforms
- Mac
- Linux
- Docker
 Israel


CVE Lite CLI is described as 'Scans JavaScript and TypeScript lockfiles, distinguishes direct and transitive issues, and generates actionable fix commands. Runs locally with offline mode' and is a vulnerability scanner in the development category. There are six alternatives to CVE Lite CLI for a variety of platforms, including Web-based, Linux, Mac, SaaS and Docker apps. The best CVE Lite CLI alternative is Trivy, which is both free and Open Source. Other great apps like CVE Lite CLI are Snyk, Dependabot, Retire.js and Patchdex.
Scanner for vulnerabilities in container images, file systems, and Git repositories, as well as for configuration issues and hard-coded secrets.
Israel
 United Kingdom


Keep your dependencies on GitHub up to date without the automatic creation of the Pull Requests to update the dependency and checking for the known vulnerabilities.
https://github.blog/2020-06-01-keep-all-your-packages-up-to-date-with-dependabot/


Patchdex is a vulnerability database and package analysis tool. It provides instant security verdicts (RED, YELLOW, GREEN), checks for active malware, flags unpatched CVEs, and monitors maintainer health (abandonware, bus factor) to help developers choose safe dependencies.


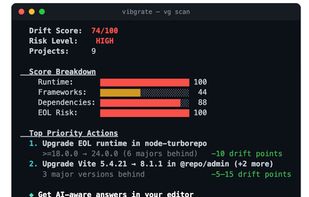
Local command-line scanner that measures dependency, framework and runtime drift, checks known vulnerability advisories, and prioritizes upgrades. It builds a code graph to trace imports and calls, assess change impact, and provide matching docs to AI assistants.
United Kingdom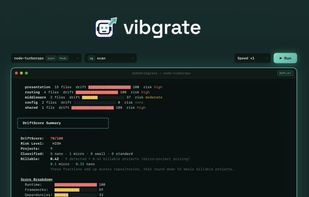


 United States

 Norway


