




PocketSOC
Like
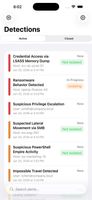
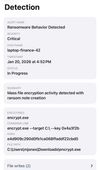
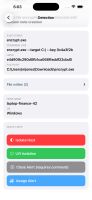
Mobile incident response app that lets SOC teams view detections, isolate hosts, and manage alerts from CrowdStrike, Microsoft Defender, and AWS GuardDuty directly from their phone.


+1

Cost / License
- Subscription
- Proprietary
Platforms
- iPhone
- iPad
- Android
- Online
- Software as a Service (SaaS)

Features

PocketSOC information
Developed by
 Jason Lazerus
Licensing
Proprietary and Commercial product.Pricing
Subscription that costs up to $599 per month.Alternatives
1 alternatives listedBadge
Get an embeddable badge for PocketSOCSupported Languages
No comments or reviews, maybe you want to be first?

