VibeGuard is a free open-source security linter built
specifically for AI-generated code.
AI coding tools like GitHub Copilot, Cursor, ChatGPT,
Claude and Gemini write code fast but they also
produce the same security vulnerabilities repeatedly
because they were trained on code that had those
mistakes in it.
VibeGuard catches them automatically before they
reach production.
What it detects:
? SQL injection via f-strings
? Hardcoded API keys and passwords
? JWT tokens without algorithm verification
? Command injection via shell=True
? MD5 and SHA1 for password hashing
? DEBUG=True shipped to production
? pickle.loads() on untrusted data
? eval() called with user input
? yaml.load() instead of safe_load()
? Path traversal via user-controlled file paths
? XML external entity injection
? CORS configured to allow all origins
? Insecure cookie configuration
? Hardcoded encryption keys
? Insecure random for security tokens
Every finding includes the exact working code
to fix the problem not a description, not a
link to documentation, but the actual replacement code.
Works on Python, JavaScript and TypeScript.
Zero configuration is needed to get started.
Grades your code A to F.
Runs in GitHub Actions automatically.
MIT licensed—completely free.
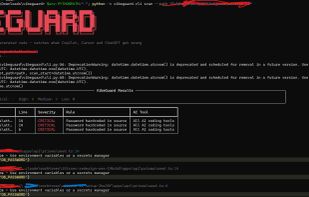
Scanned a real production codebase and found
3 critical vulnerabilities missed by the existing
security pipeline, all from AI-generated code,
all fixed with exact one-line commands.





 EU


 David Seagal
 David Seagal


