ooshare.io icon
ooshare.io icon

ooshare.io

Provides AES-256-GCM in-browser encryption for text and files, enabling single-use, self-destructing links with no account needed, open source MIT, up to 50,000 characters or 10 MB, keys only in URL, auto-expires in 1–72 hours, and atomic deletion upon access.
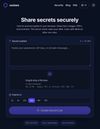
 The landing page is the tool itself. Paste a password or API key into the text area, or drag in a file up to 10 MB — images, PDFs, or archives. Choose when it expires (1–72 hours), and get a link that self-destructs after one view — encrypted in your browser before it ever reaches the server.
 The landing page is the tool itself. Paste a password or API key into the text area, or drag in a file up to 10 MB — images, PDFs, or archives. Choose when it expires (1–72 hours), and get a link that self-destructs after one view — encrypted in your browser before it ever reaches the server.

Cost / License

  • Free
  • Open Source (MIT)

Platforms

  • Online
0likes
0articles

Features

ooshare.io News & Activities

Highlights All activities

Recent activities

ooshare.io information

AlternativeTo Categories

Security & PrivacyFile SharingDevelopment

GitHub repository

  •  2 Stars
  •  0 Forks
  •  0 Open Issues
  •   Updated  
View on GitHub

Popular alternatives

View all
ooshare.io was added to AlternativeTo by diogohudson on and this page was last updated .
No comments or reviews, maybe you want to be first?

Official Links

What is ooshare.io?

Sending a password by email, Slack, or text leaves it sitting in someone's inbox forever â?? a standing breach risk long after the handoff. Only Once Share sends passwords, API keys, screenshots, PDFs, and archives as a single link that self-destructs after one view.

Unlike tools like OneTimeSecret or Privnote, encryption happens entirely in your browser. Your text and files are sealed with AES-256-GCM before they ever leave your device, and the decryption key lives only in the URL fragment â?? which browsers never send to any server. The server stores ciphertext it cannot read, and can't even tell a text secret from an image or a ZIP file. Even a total server compromise leaves your secrets unreadable.

When the recipient opens the link, the data is retrieved and atomically deleted in a single operation â?? there is no window for a second read. Links also auto-expire in 1â??72 hours, so nothing persists beyond what you choose.

Free, no account, no limits: text up to 50,000 characters and files up to 10 MB (images, PDF, ZIP, RAR, 7Z, TAR.GZ). Fully open source under MIT â?? audit the crypto yourself or self-host with Docker. Available in 6 languages.